By default, depending on file permissions, WordPress automatically will modify the contents of your site’s .htaccess file. It does this on several occasions, adding and/or updating the rewrite rules required for WP’s permalink functionality. This post explains how this works, why it can be dangerous, and how to stop it from happening. Continue reading »

After months of preparation and production, my new video course on developing secure WordPress sites is now available at Lynda.com. This is my second video course on securing WordPress; the first one was originally launched in 2011 and remained in Lynda’s library for over five years. I received a lot of great feedback on the course, and so I jumped on the opportunity to do another one. If there is one thing that I enjoy doing, it’s helping people with […] Continue reading »
Years ago, I thought the whole humans.txt thing was just silly, and even explained how to block humans.txt requests. But the concept actually has grown on me to the point where I now include a customized humans.txt file for most of my projects. It just seems like some useful information to make available for those who are looking for it. You know, all about the site, author, team, and such. And I have seen plenty of requests for humans dot […] Continue reading »

This tutorial explains how to block user-enumeration scans in WordPress. As explained in greater depth here, user enumeration happens when some malicious script scans a WordPress site for user data by requesting numerical user IDs. For example, requests for author=1 through some number, say, author=1000, may reveal the usernames for all associated users. With a simple enumeration script, an attacker can scan your site and obtain a list of login names in a matter of seconds. Continue reading »

This quick post explains how to stop the notorious site scrapers, RSSing.com, from stealing your content. In fact, this technique can be used to stop virtually any site that uses HTML frames to scrape your pages. Once again, the solution is one line of .htaccess to the rescue. Continue reading »

Image courtesy of eChunks.com Here is a quick security tip for people using popular apps on the Web. That is, apps like WordPress that may be widely used and targeted by bad actors and/or automated scripts. It’s all about adding another layer of security by hardening admin-level usernames.. Every now and then, I get an email letting me know that someone has requested a password reset for one of my admin-level WordPress accounts. Usually, the email notifications are sent directly […] Continue reading »
I recently switched over to Panic’s Coda 2 for code editing and SFTP functionality. After using my previous editor/FTP software for over 10 years, I was surprised that learning Coda 2 happened so easily. It literally took me like two days of using it before I was back up to full development speed. In the process of learning, I discovered numerous questions and concerns that weren’t covered in the Coda 2 documentation or anywhere online. This post rounds up these […] Continue reading »
It seems the WordPress xmlrpc.php file is the target of another type of attack. Before, it was the XML-RPC Pingback Vulnerability. Now, it is the Brute Force Amplification Attack. This post explains what you need to know and then cuts to the chase with several ways to protect your site against this new malicious exploit, as well as all other related threats. Continue reading »
Over the years, my sites have been hacked numerous times. Each hacking event was somewhat of a miserable experience at first, but ultimately educational and even enlightening. I’m not going to say that getting hacked was the best thing that ever happened to me, but it certainly wasn’t the end of the world. In this post, I want to share some important steps to take and things to keep in mind if and when you discover that your site has […] Continue reading »
One of the most annoying, persistent scans I’ve seen in a long time are those hunting for the revslider vulnerability. In the five or so months since the exploit was discovered, many sites have been compromised. And based on what I’ve been seeing in my traffic logs, the risk is far from over. Apparently every 2-bit script kiddie and their pet hamster wants a piece of the “revslider action”. Continue reading »

Whether you like it or not, there are scripts and bots out there hammering away at your sites with endless HTTP “POST” requests. POST requests are sort of the opposite of GET requests. Instead of getting some resource or file from the server, data is being posted or sent to it. To illustrate, normal surfing around the Web involves your browser making series of GET requests for all the resources required for each web page. HTML, JavaScript, CSS, images, et […] Continue reading »

Just a quick post with some tips for troubleshooting and testing HTTP requests. For example, if you have a plugin that sends requests behind the scenes via Ajax or cURL or whatever, it’s nice to have a way to view request details such as headers, the response, and everything in between. This article is aimed primarily at WordPress users, but contains more general tips and tricks as well. Continue reading »
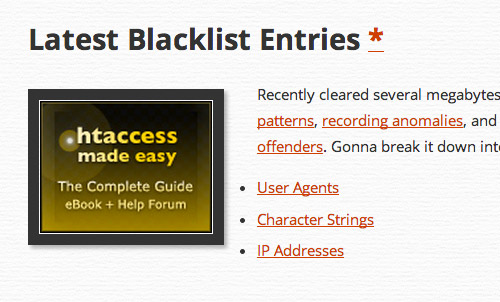
If you’re displaying floated images in your posts, you may notice that margins of lists and other block-level elements seem to “collapse”, as shown in this screenshot from the 2013 redesign: Continue reading »

Wrapping up 2012, I finally launched xyCSS, which is all about responsive, grid-based design. To showcase xy.css, I used it to design WP-Mix.com, which also serves to house a growing collection of choice code snippets. Currently WP-Mix features over 100 snippets, tutorials, and other useful bits to help with WordPress development and web design in general. The topics are similar to those at Perishable Press (e.g., WordPress, PHP, JavaScript, CSS, etc.), but the posts are less-involved and aimed at intermediate […] Continue reading »
It was recently reported about a WordPress Pingback Vulnerability, whereby an attacker has four potential ways to cause harm via xmlrpc.php, which is the file included in WordPress for XML-RPC Support (e.g., “pingbacks”). In this post, I offer a simple .htaccess technique to lock things down and protect against any meddling via the xmlrpc.php file. Continue reading »
Just as there are specifications for designing with CSS, HTML, and JavaScript, there are specifications for working with URIs/URLs. The Internet Engineering Task Force (IETF) clearly defines these specifications in RFC 3986: Uniform Resource Identifier (URI): Generic Syntax. Within that document, there are guidelines regarding which characters may be used safely within URIs. This post summarizes the information, and encourages developers to understand and implement accordingly. Continue reading »
 Perishable Press is operated by Jeff Starr, a professional web developer and book author with two decades of experience.
Here you will find posts about web development, WordPress, security, and