Whenever I find myself working with PHP or messing around with server settings, I nearly always create a phpinfo.php file and place it in the root directory of whatever domain I happen to be working on. These types of informational files employ PHP’s handy phpinfo() function to display a concise summary of all of your server’s variables, which may then be referenced for debugging purposes, bragging rights, and so on. While this sort of thing is normally okay, I frequently […] Continue reading »

Stolen content is the bane of every blogger who provides a publicly available RSS feed. By delivering your content via feed, you make it easy for scrapers to assimilate and re-purpose your material on their crap Adsense sites. It’s bad enough that someone would re-post your entire feed without credit, but to use it for cheap money-making schemes is about as pathetic as it gets. If you’re lucky, the bastards may leave all the links intact, so at least you […] Continue reading »
The shared server on which I host Perishable Press was recently scanned by security software that revealed a significant security risk. Namely, the HTTP request methods TRACE and TRACK were found to be enabled on my webserver. The TRACE and TRACK protocols are HTTP methods used in the debugging of webserver connections. Although these methods are useful for legitimate purposes, they may compromise the security of your server by enabling cross-site scripting attacks (XST). By exploiting certain browser vulnerabilities, an […] Continue reading »

In my article, Associate Extensionless Files with Notepad, I explain how to navigate the labyrinthine maze of Windows dialogue menus to assign Microsoft’s Notepad text editor as the opening application for files without extensions. In this post, I’ll show you how to associate any file type with any program (including Notepad) in less than five seconds. Ready? Don’t blink, you’ll miss it.. ;) Continue reading »
Normally, when visitors post a comment to your site, specific types of client data are associated with the request. Commonly, a client will provide a user agent, a referrer, and a host header. When any of these variables is absent, there is good reason to suspect foul play. For example, virtually all browsers provide some sort of user-agent name to identify themselves. Conversely, malicious scripts directly posting spam and other payloads to your site frequently operate without specifying a user […] Continue reading »

Taking screenshots of DVD, MPEG, AVI, and other video on Windows machines requires a couple of extra steps. A normal screenshot is easy enough to capture by pressing the “Print Screen” button on your keyboard. To capture a screenshot of video display, however, you need to disable hardware acceleration to make it work. To do this on Windows machines, go to your Desktop properties and click on the Settings tab. Click on the Advanced button and then on the Troubleshooting […] Continue reading »
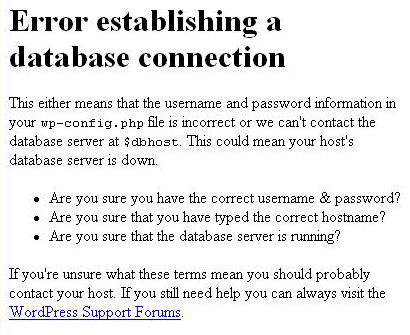
The other day, my server crashed and Perishable Press was unable to connect to the MySQL database. Normally, when WordPress encounters a database error, it delivers a specific error message similar to the following: Continue reading »
Given my propensity to discuss matters involving error log data (e.g., monitoring malicious behavior, setting up error logs, and creating extensive blacklists), I am often asked about the best way to go about monitoring 404 and other types of server errors. While I consider myself to be a novice in this arena (there are far brighter people with much greater experience), I do spend a lot of time digging through log entries and analyzing data. So, when asked recently about […] Continue reading »
You have seen user-agent blacklists, IP blacklists, 4G Blacklists, and everything in between. Now, in this article, for your sheer and utter amusement, I present a collection of over 8000 blacklisted referrers. Shortcut: skip the article and jump to Disclaimer and Download » Referrer Spam Sucks For the uninitiated, in teh language of teh Web, a referrer is the online resource from whence a visitor happened to arrive at your site. For example, if Johnny the Wonder Parrot was visiting the […] Continue reading »

As discussed in my recent article, Eight Ways to Blacklist with Apache’s mod_rewrite, one method of stopping spammers, scrapers, email harvesters, and malicious bots is to blacklist their associated user agents. Apache enables us to target bad user agents by testing the user-agent string against a predefined blacklist of unwanted visitors. Any bot identifying itself as one of the blacklisted agents is immediately and quietly denied access. While this certainly isn’t the most effective method of securing your site against […] Continue reading »

At last! After many months of collecting data, crafting directives, and testing results, I am thrilled to announce the release of the 4G Blacklist! The 4G Blacklist is a next-generation protective firewall that secures your site against a wide range of automated attacks and other malicious activity. Continue reading »

Last year, after much research and discussion, I built a concise, lightweight security strategy for Apache-powered websites. Prior to the development of this strategy, I relied on several extensive blacklists to protect my sites against malicious user agents and IP addresses. Unfortunately, these mega-lists eventually became unmanageable and ineffective. As increasing numbers of attacks hit my server, I began developing new techniques for defending against external threats. This work soon culminated in the release of a “next-generation” blacklist that works […] Continue reading »

One of the original purposes of Perishable Press involved serving as a “virtual dumpster” for all of my miscellaneous code snippets. Over time, I continued elaborating to greater degrees on the various code recipes that I was posting, until eventually those brief snippet posts evolved into complete, richly detailed articles (at least from my point of view). Now that I enjoy the luxury of writing for an incredible audience, I try to avoid posting anything that doesn’t include an accompanying […] Continue reading »

As my browser of choice, Firefox provides all the functionality I need for web design, application development, everyday surfing, and much more. With a handful of choice extensions installed, Firefox is a lean, mean “get-it-done” machine. Plus, I am always looking for new ways to boost productivity and increase efficiency. Of course, an excellent way to do this involves learning and using as many mouse and keyboard shortcuts as possible. Over the past few years, I have collected oodles of […] Continue reading »

This is great. A couple of weeks ago I twittered that I had canceled my LinkedIn account. Without going into detail, suffice it to say that my original account signup information was no longer valid and the LinkedIn support staff was unable to even locate my account, let alone reset my password or provide login access. I know the account was there, but no matter what I tried I could not login. So, without being able to update my information, […] Continue reading »
Monitoring your computer’s Internet activity is a powerful tool, enabling you to: keep an eye on background processes reveal viruses and other malware expose unauthorized access monitor running programs log process activity ..and much more. The best part? It’s super-easy. Here’s how I do it on Win XP: Open the command prompt and type “netstat -n 5 > scan.txt” After a minute or two (or any amount of time), press Ctrl+C to stop monitoring Type “scan.txt” to open the log […] Continue reading »
 Perishable Press is operated by Jeff Starr, a professional web developer and book author with two decades of experience.
Here you will find posts about web development, WordPress, security, and