
After three years of development, testing, and feedback, I’m pleased to announce the official launch version of the 6G Firewall (aka the 6G Blacklist). This version of the nG Firewall is greatly refined, heavily tested, and better than ever. Fine-tuned to minimize false positives, the 6G Firewall protects your site against a wide variety of malicious URI requests, bad bots, spam referrers, and other attacks. Blocking bad traffic improves site security, reduces server load, and conserves precious resources. The 6G […] Continue reading »
Over the years, my sites have been hacked numerous times. Each hacking event was somewhat of a miserable experience at first, but ultimately educational and even enlightening. I’m not going to say that getting hacked was the best thing that ever happened to me, but it certainly wasn’t the end of the world. In this post, I want to share some important steps to take and things to keep in mind if and when you discover that your site has […] Continue reading »
I use s2member (free version) and s2member Pro on a few of my sites. Have been for several years now. Over the course of time, I have amassed a healthy collection of notes, code snippets and techniques for customizing default functionality, adding features, and so forth. Gonna post the collection online for the benefit of any others who may be seeking for similar modifications and/or related information. Continue reading »
One of the most annoying, persistent scans I’ve seen in a long time are those hunting for the revslider vulnerability. In the five or so months since the exploit was discovered, many sites have been compromised. And based on what I’ve been seeing in my traffic logs, the risk is far from over. Apparently every 2-bit script kiddie and their pet hamster wants a piece of the “revslider action”. Continue reading »
BBQ Firewall is a lightweight, super-fast plugin that protects your site against a wide range of threats. BBQ checks all incoming traffic and quietly blocks bad requests containing nasty stuff like eval(, base64_, and excessively long request-strings. This is a simple yet solid solution for sites that are unable to use a strong Apache/.htaccess firewall. Continue reading »
Book Launch! My fourth book, WordPress Themes In Depth, focuses entirely on WordPress theme development. It goes in-depth on how to build, customize, and distribute your own WordPress themes. It’s 10+ years of experience with WordPress jam-packed into 450 pages of non-stop theme-building action. Continue reading »
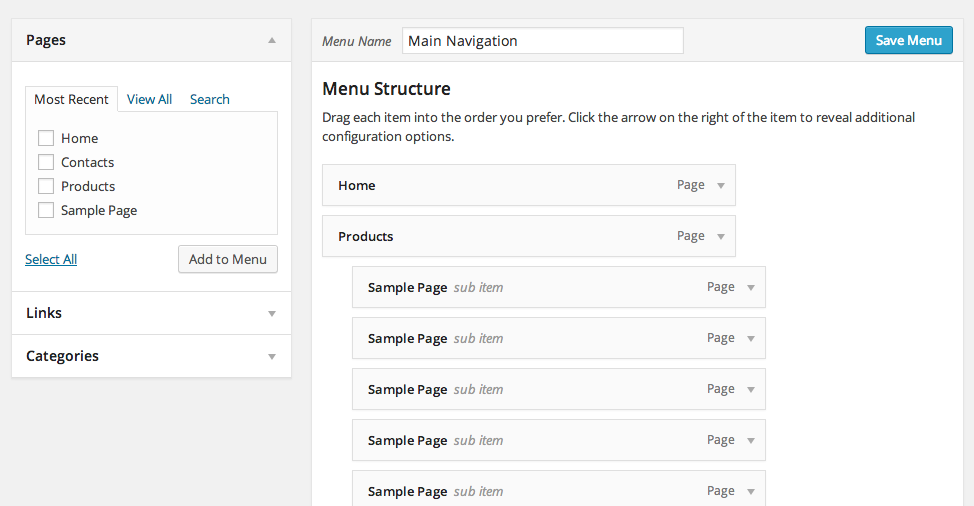
In this tutorial I am going to show you how to build a pure CSS drop down menu in WordPress. I will walk you through the steps of creating a menu in WordPress, customizing it with CSS, and then printing the menu in your theme file. This tutorial requires that you have access to edit your WordPress theme files and also a basic understanding of HTML and CSS. I will walk through the process step-by-step so don’t worry if you […] Continue reading »

Whether you like it or not, there are scripts and bots out there hammering away at your sites with endless HTTP “POST” requests. POST requests are sort of the opposite of GET requests. Instead of getting some resource or file from the server, data is being posted or sent to it. To illustrate, normal surfing around the Web involves your browser making series of GET requests for all the resources required for each web page. HTML, JavaScript, CSS, images, et […] Continue reading »
I woke up this morning to the sound of thousands of 404 requests hitting the server. It’s sad that there are kiddies out there who have nothing better to do than buy some pathetic $50 script and then sit there like an imbecile harassing people for hours on end. But alas, that is the world we live in — fortunately it’s less than trivial to block the entire scan with just a few lines of good old .htaccess. Continue reading »

Just a quick post with some tips for troubleshooting and testing HTTP requests. For example, if you have a plugin that sends requests behind the scenes via Ajax or cURL or whatever, it’s nice to have a way to view request details such as headers, the response, and everything in between. This article is aimed primarily at WordPress users, but contains more general tips and tricks as well. Continue reading »

Over the past several months, I’ve assembled a “micro” blacklist to keep some recent threats at bay. Eventually, this will be integrated into the next nG Blacklist, but for now I just wanted to post and share with anyone else who is actively monitoring their server logs and aware of the recent spike in malicious activity. Continue reading »
Another update! This time to the vanilla/PHP version of my Ajax Error Log. As with the new WordPress version, this update improves the script’s design, performance, and security. Continue reading »
New version of Ajax-Powered Error Logs for WordPress now available for download. The functionality is the same, but the script is rewritten for better design, performance, and security. Continue reading »

The 2013 User Agent Blacklist blocks hundreds of the worst bots while ensuring open-access for normal traffic, major search engines (Google, Bing, et al), good browsers (Chrome, Firefox, Opera, et al), and everyone else. Compared to blocking threats by IP, blocking by user-agent is more effective as a general security strategy. Although it’s trivial to spoof any user agent, many bad requests continue to report user-agent strings that are known to be associated with malicious activity. For example, the notorious […] Continue reading »
When time allows, I like to post my collections of the worst IP addresses for the current year. Certainly, there are pros and cons to using an IP blacklist. In general, IPs are easily spoofed, change frequently, and are therefore unreliable as a general security strategy. But as a short-term solution, IP blacklists serve as an excellent method for dealing with specific and/or ongoing threats and attacks. Continue reading »

It’s been quiet around here, but I have a good excuse. I spent the last six months writing, designing, and publishing my third book, The Tao of WordPress. This is an excellent book for beginners, students, designers, and basically anyone who wants to learn how to get the most from WordPress. The book “soft-launched” last week, and now I want to share the news with readers here at Perishable Press. Continue reading »
 Perishable Press is operated by Jeff Starr, a professional web developer and book author with two decades of experience.
Here you will find posts about web development, WordPress, security, and
