How to streamline and maximize the effectiveness of your WordPress URLs by using htaccess to remove extraneous post-date information: years, months, and days.. Recently, there has been much discussion about whether or not to remove the post-date information from WordPress permalinks1. Way back during the WordPress 1.2/1.5 days, URL post-date inclusion had become very popular, in part due to reports of potential conflicts with post-name-only permalinks. Throw in the inevitable “monkey-see, monkey-do” mentality typical of many bloggers, and suddenly an […] Continue reading »
In my previous articles on PHP error handling, I explain the process whereby PHP error handling may be achieved using htaccess. Handling (logging, reporting) PHP errors via htaccess requires the following: Continue reading »
Here is an example of one of the most frequently asked PHP/htaccess-related questions I receive here at Perishable Press: How do I redirect a specific page/URL using PHP/htaccess? So common is this inquiry that I have decided to just post a quick, “one-minute” tutorial describing the technique. Continue reading »

Permalink URL canonicalization is automated via PHP in WordPress 2.3+, however, for those of us running sites on pre-2.3 versions or preferring to deal with rewrites directly via Apache, comprehensive WordPress URL canonicalization via htaccess may seem impossible. While there are several common methods that are partially effective, there has not yet been available a complete, user-friendly solution designed specifically for WordPress. Until now.. In this article, I share my “secret” htaccess URL canonicalization formula. I originally developed this method […] Continue reading »
In my previous article on logging PHP errors, How to Enable PHP Error Logging via htaccess, we observed three fundamental aspects of preventing, preserving, and protecting your site’s PHP errors. Continue reading »

Welcome to the Perishable Press “Blacklist Candidate” series! In this first post, we begin a new tradition of exposing, humiliating and banishing spammers, crackers and other worthless scumbags.. Every Wednesday, I take a little time to investigate my 404 error logs. In addition to spam, crack attacks, and other deliberate mischief, the 404 logs for Perishable Press contain errors due to missing resources, mistyped URLs, and the occasional bizarre or even suspicious behavior of the search-engine robots. Whenever possible, I […] Continue reading »

In this article, I present a simple method for dramatically decreasing the size of your WordPress database by partially emptying old data from the WP-ShortStat table via the following SQL command: DELETE FROM `wp_ss_stats` ORDER BY `id` ASC LIMIT n That simple SQL query will truncate n number of rows from a database table named wp_ss_stats. You can of course change the table name and number of rows to whatever is needed. And that is the point of this entire […] Continue reading »
Recently, while attempting to optimize site performance, I found myself experimenting with various caching mechanisms currently available for WordPress. Specifically, I explored each of the following caching options: Continue reading »
In this brief tutorial, I will show Apache users how to suppress PHP errors from visitors and enable PHP error logging via htaccess. Tracking your site’s PHP errors is an excellent way to manage and troubleshoot unexpected issues related to plugins and themes. Even better, monitoring PHP errors behind the scenes via private log is far better than trying to catch them as they appear at random visits. Thanks to the magical powers of htaccess, there is an easy way […] Continue reading »
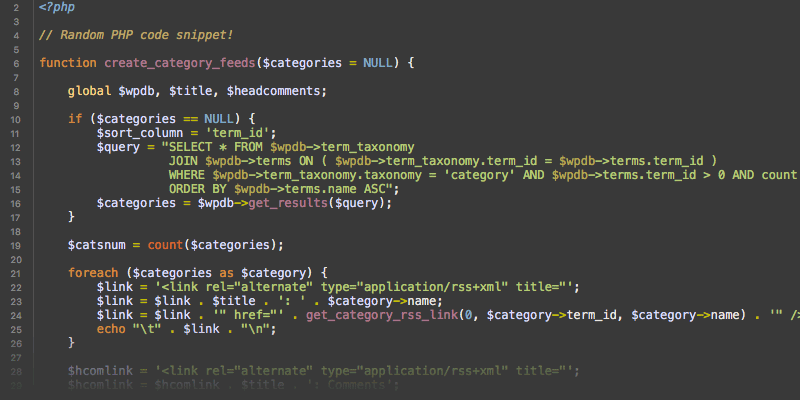
A great to way to share your PHP code with visitors is to display it directly in the browser with automatically generated syntax highlighting. Here is a screenshot showing an example of syntax-highlighted PHP code: Displaying your PHP scripts in syntax-highlighted form is an excellent way to share source code details directly with your readers. Rather than zipping the script and requiring users to download, unzip, and open the file in an editor, displaying your code directly saves you and […] Continue reading »
In this brief article I explain the atrocity that is UserCash and then provide the JavaScript needed to protect your site. Continue reading »
After implementing any of the hotlink-prevention techniques described in our previous article, you may find it necessary to disable hotlink-protection for a specific directory. By default, htaccess rules apply to the directory in which it is located, as well as all subdirectories contained therein. There are (at least) three ways to enable selective hotlinking: Place hotlink images in an alternate directory This method works great if your hotlink-protection rules are located in a directory other than the site root. Simply […] Continue reading »
In this brief tutorial, we are going to enable users to access any file or directory of a site that is password-protected via htaccess. There are many reasons for wanting to employ this technique, including: Share public resources from an otherwise private site Enable visitors to access content during site maintenance Testing and formatting of layout and design during development As a webmaster, I have used this technique on several occasions. This trick works great for allowing access to any […] Continue reading »
In this article, I present several heavily commented examples of WordPress loops. I have found that many readers appreciate these types of loop examples, as it helps them to understand how the loop works while enabling them to easily copy, paste, and adapt the code for their own purposes. In our first example, we examine a basic WordPress loop. When implemented, this loop will display “x” number of posts, where “x” represents the number specified via the WordPress Admin reading […] Continue reading »
While planning my current site renovation project, I considered changing the format of my permalinks. Reasons for modifying the permalink structure of a site include: Continue reading »

In our original htaccess blacklist article, we provide an extensive list of bad user agents. This so-called “Ultimate htaccess Blacklist” works great at blocking many different online villains: spammers, scammers, scrapers, scrappers, rippers, leechers — you name it. Yet, despite its usefulness, there is always room for improvement. Continue reading »
 Perishable Press is operated by Jeff Starr, a professional web developer and book author with two decades of experience.
Here you will find posts about web development, WordPress, security, and
